The Japanese keyword hack, the pharma hack and the redirect hack, explained.
Google shows pages in Japanese under your name. Or drug ads. Or customers say your site sent them somewhere strange, and you cannot make it happen yourself. These are three different infections with one goal: borrowing your domain’s reputation. Here is how to tell them apart and get rid of them properly.
Or call or text (502) 387-1142
Websites I have built for Kentucky businesses

The short answer
The Japanese keyword hack creates thousands of new pages of auto-generated Japanese text on your domain. The pharma hack injects prescription-drug spam into your pages or database, usually shown only to search engines. The redirect hack sends some of your visitors to another site, often only on phones or only when they arrive from Google.
All three are usually hidden from you on purpose, all three need the same core cleanup (find the code, remove it from known-good copies, close the way in, change every password), and all three need a second job afterward: telling Google the spam is gone.
First, find out which one you have
You often cannot see these hacks by visiting your own site, because they are built to hide from the owner. Look where they show up instead.
- Search Google for site:yourdomain.com. Scroll several pages. Japanese titles, drug names, knock-off brand goods or casino terms under your domain tell you a lot.
- Search your domain with drug terms, such as your domain plus viagra or cialis. Pharma spam often only appears for those searches.
- Open Search Console’s Security Issues report. Google labels hacked sites by type: content injection (spam text or links added to your pages), code injection (malicious code such as redirects added to your pages) and URL injection (new spam pages created on your site).
- Check for browser warnings. A red screen in Chrome means Google has flagged the site for visitors too; see the Deceptive site ahead warning.
- Use the URL Inspection tool on a suspicious address. It shows what Google’s crawler receives, which may be very different from what your browser shows.
- Test like a stranger. Open your site from a Google result, on a phone, in a private window, logged out. That is the visit a redirect hack is waiting for.
Write down what you find, with screenshots and times. You will need it for the cleanup and for Google’s review request.
The Japanese keyword hack
What it looks like
Google’s own guide to the Japanese keyword hack describes it plainly: pages of autogenerated Japanese text appear on your site in randomly named folders, each carrying affiliate links to stores selling fake brand merchandise. There can be thousands of them. Visit one yourself and you may get a 404 or what looks like a normal page, because the hack uses cloaking to show the spam only to search engines.
The part people miss
Attackers often verify themselves as an owner of your site in Google Search Console, so they can change settings such as geotargeting and submit their own sitemaps. If you ever got an email saying someone new verified your site, take it seriously.
Cleaning it up
- Remove any Search Console owners you do not recognize, and delete their verification token. Google notes it may be an HTML file on your server or a rule in .htaccess that generates one on request.
- Replace .htaccess with a clean default copy. These hacks often rewrite it to route the spam pages.
- Reinstall WordPress core, plugins and themes from official packages.
- Look for the generator: recently changed or unusually large PHP files, and obfuscated code using functions such as base64_decode, eval and gzinflate.
- Remove spam entries from your sitemaps, and delete any sitemap that contains only spam.
The pharma hack
What it looks like
Search results for your site show prescription drug names, while your pages look normal to you. Sucuri, a security firm that cleans these infections, describes it as SEO spam that injects pages or content targeting drug keywords so search engines index them under your domain. The spam is usually cloaked: search engines get the drug content and people get your real page.
Where it hides
The pharma hack rarely lives in one place. Expect several layers:
- spam stored in the database, often in the posts table, sometimes woven into your own existing text
- modified plugin or theme files that insert the spam as pages are built
- files named to look like WordPress core files, placed in the wrong folders
- back doors that let the attacker put it all back after a partial cleanup
- administrator accounts you did not create
Cleaning it up
Remove every layer in one pass. Fixing the visible injection while the database entries or the back door survive is the classic reason a pharma hack returns a week later. Replace core, plugin and theme files from clean copies, clean the database carefully because the spam may sit inside real content, delete unknown admin users, and only then request Google’s review.
The redirect hack
What it looks like
Some visitors land on a scam, gambling or adult site instead of yours. Google’s spam policies describe exactly this: injected code that sends some users to harmful or spammy pages, with the redirect depending on the referrer, the browser or the device. The classic pattern sends mobile visitors arriving from a Google result away, while desktop visitors and anyone typing your address directly see the real site.
That is why the owner is usually the last to know. You are logged in, on a desktop, typing your own address. The hack leaves you alone.
Where it hides
- JavaScript injected into pages, often in the header or footer, inside a widget, or appended to a theme or plugin script file.
- Server rules in .htaccess that check the referrer or user agent before redirecting.
- Database entries such as site options or post content carrying a script tag.
- PHP files in the uploads folder, where executable code should never be.
Cleaning it up
Compare every file against clean packages, search the database for script tags and unfamiliar domains, check .htaccess line by line, and remove anything executable from uploads. Then test again the way the hack expects: a phone, a private window, a click from a Google result.
What all three have in common
Each of these hacks is a symptom. The cleanup that lasts answers how the attacker got in as well as what they left behind. In my experience the answer is usually one of three: a plugin that was out of date, a password that was reused or weak, or a second compromised site on the same hosting account.
WordPress.org’s FAQ My site was hacked and Google’s help for hacked sites both set out this order of work. A proper cleanup, whichever hack you have:
- Keep a copy of the infected site first. It is the evidence of how they got in.
- Replace files from clean copies. Core, plugins and themes come back from official packages. Hand-editing infected files misses things.
- Clean the database of injected content, rogue users and hidden options.
- Close the door. Update or remove the vulnerable plugin, and change every credential: WordPress users, hosting, database, SFTP and any API keys.
- Put a firewall and monitoring in front, so a repeat raises an alert instead of a phone call from a customer.
One-click cleaner plugins find known signatures. They rarely find a back door hidden in a file that looks normal, which is why a site cleaned that way so often gets reinfected.
Getting the spam out of Google
Cleaning the server does not clean the search results. Google keeps crawling the spam addresses for weeks after the files are gone, so what those addresses return matters.
- Answer spam URLs with 410 Gone. A 410 tells Google the page is gone for good. Do not redirect spam addresses to your home page, which tells Google they are still alive.
- Redirect real old pages with a 301 to the page that replaces them.
- Submit a clean sitemap and request indexing for your real pages.
- Request a review in the Security Issues report once the site is genuinely clean. Google’s Security Issues help says a review can take from a few days to a few weeks, and asks you not to resubmit while one is pending. A good request explains the problem, the steps taken and the result.
The full sequence, with a real physician site as the example, is in my guide to hacked website recovery and Google cleanup.
When a rebuild beats a cleanup
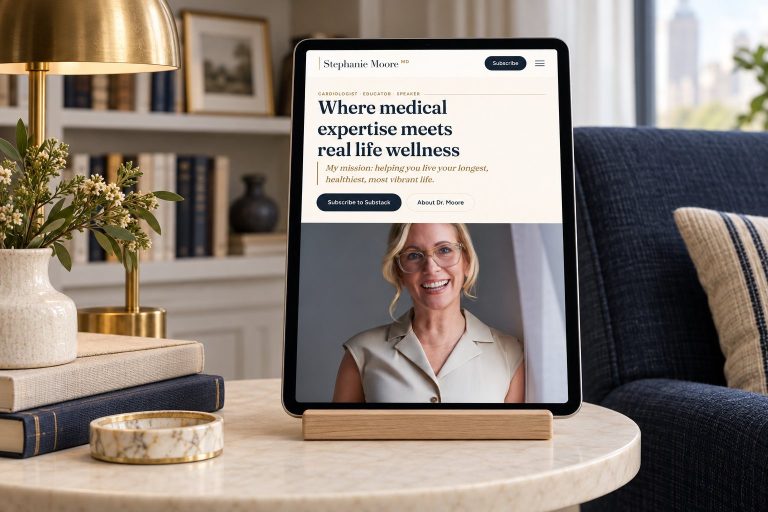
If the site is old, built by someone who is no longer around, running abandoned plugins, or has been reinfecting itself for months, a forensic cleanup can cost more than replacing it. In that case I keep the domain and the real URLs, and rebuild everything behind them on a clean, current install, as I did for Dr. Stephanie Moore’s website.
Either way, the first step is the same: do not delete anything yet, and follow what to do in the first hour. When you are ready for the cleanup itself, that is my WordPress malware removal service, run by the same Louisville developer who then hosts and watches the site.
Frequently asked questions
Why can’t I see the spam when I visit my own site?
Because the hack is built to hide from you. Cloaking shows the spam only to search engines, and redirect hacks often skip logged-in users, desktop visitors and people who type the address. Use Google’s URL Inspection tool and a logged-out phone visit to see what others see.
Can I just delete the spam pages?
Deleting the pages removes the symptom. The code that generates them, and the way the attacker got in, are still there, so the pages come back. The generator, the back doors and the entry point all have to go.
Will a security plugin clean it up?
A security plugin can help detect an infection. It will not change your passwords, close the vulnerable plugin or clean Google’s index, and scanners often miss back doors hidden in normal-looking files.
How long until the spam disappears from Google?
Weeks. Google rechecks the old spam addresses on its own schedule. Returning 410 for them and requesting a review speeds it up, but expect to keep checking for at least six weeks on a site with a lot of spam.
Do I need a new domain?
Almost never. The spam is attached to addresses on your domain, not the domain itself. A clean site that answers those addresses correctly clears it, and your name keeps the history it has earned.
A physician’s name, cleared of shopping and gambling spam.
Dr. Stephanie Moore’s old website had been compromised, and Google was showing gambling and shopping spam under her name, including spam pages served through odd query strings on the home page.
I rebuilt the site on a clean install, answered every known spam pattern with a 410, redirected her real old pages, locked the login to the edge network and launched with scheduled backups and a firewall in front. After relaunch, Security Issues and Manual Actions both read clean.

Seeing spam under your name?
Send me your domain and a screenshot of what Google shows. I will tell you which hack it looks like and what a proper cleanup takes, before you pay for anything.